


Get SC-300 Actual Free Exam Q&As to Prepare for Your Microsoft Certification
Microsoft Actual Free Exam Questions And Answers
Why is the Microsoft SC-300 Certification Exam difficult to write?
Microsoft SC-300 exam is a challenging exam. To get a high score, you must be prepared for the exam. You must ensure that you have sufficient knowledge of the exam subjects. Microsoft SC-300 Dumps helps you prepare for this exam by providing practice test questions for the exam. Practice tests are available for different Microsoft Identity and Access Administrator exam certifications. The Microsoft SC-300 exam preparation guide includes detailed information about the topics and concepts covered on the actual Microsoft SC-300 exam. It also includes a test engine that simulates the real Microsoft SC-300 exam scenario. Our practice exams are designed to test your knowledge of various technologies used in the Identity and Access Management environment. Understand the technology from different perspectives, such as an administrator, engineer, or system administrator. Verified by Microsoft professionals, our study guides and practice exams are updated regularly to ensure that they accurately reflect the latest changes in the Microsoft SC-300 exam curriculum. Sources and technologies used in the Microsoft SC-300 exam are constantly changing. Team guides help you prepare for these changes by identifying the changes in the exam and creating guides that are aligned with the latest exam topics.
NEW QUESTION 23
You have an Azure Active Directory (Azure AD) tenant that contains a user named User1 and the groups shown in the following table.
In the tenant you create the groups shown in the following table.
Which members can you add to GroupA and GroupB? To answer, select the appropriate options in the answer are a. NOTE; Each correct selection is worth one point.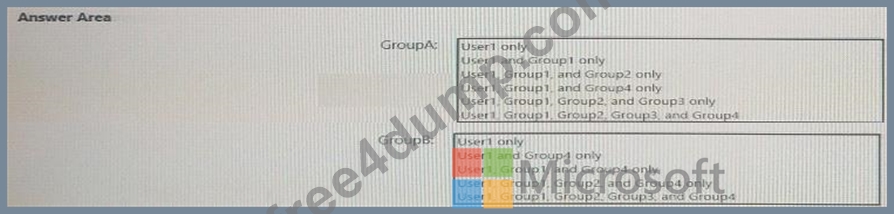
Answer:
Explanation: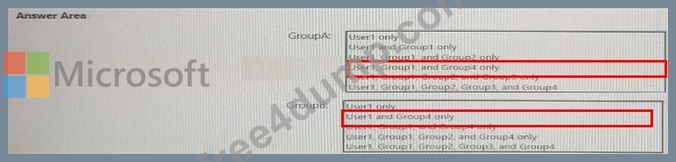
NEW QUESTION 24
You need to meet the technical requirements for the probability that user identifies were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 25
You need to track application access assignments by using Identity Governance. The solution must meet the delegation requirements.
What should you do first?
- A. Create a program.
- B. Modify the User consent settings for the enterprise applications.
- C. Create a catalog.
- D. Modify the Admin consent requests settings for the enterprise applications.
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-overview Overview Contoso, Ltd is a consulting company that has a main office in Montreal offices in London and Seattle.
Contoso has a partnership with a company named Fabrikam, Inc Fabcricam has an Azure Active Diretory (Azure AD) tenant named fabrikam.com.
Existing Environment
The on-premises network of Contoso contains an Active Directory domain named contos.com. The domain contains an organizational unit (OU) named Contoso_Resources. The Contoso_Resoureces OU contains all users and computers.
The Contoso.com Active Directory domain contains the users shown in the following table.
Microsoft 365/Azure Environment
Contoso has an Azure AD tenant named Contoso.com that has the following associated licenses:
Microsoft Office 365 Enterprise E5
Enterprise Mobility + Security
Windows 10 Enterprise E5
Project Plan 3
Azure AD Connect is configured between azure AD and Active Directory Domain Serverless (AD DS). Only the Contoso Resources OU is synced.
Helpdesk administrators routinely use the Microsoft 365 admin center to manage user settings.
User administrators currently use the Microsoft 365 admin center to manually assign licenses, All user have all licenses assigned besides following exception:
The users in the London office have the Microsoft 365 admin center to manually assign licenses. All user have licenses assigned besides the following exceptions:
The users in the London office have the Microsoft 365 Phone System License unassigned.
The users in the Seattle office have the Yammer Enterprise License unassigned.
Security defaults are disabled for Contoso.com.
Contoso uses Azure AD Privileged identity Management (PIM) to project administrator roles.
NEW QUESTION 26
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains a user named User1.
User1 has the devices shown in the following table.
On November 5, 2020, you create and enforce terms of use in contoso.com that has the following settings:
Name: Terms1
Display name: Contoso terms of use
Require users to expand the terms of use: On
Require users to consent on every device: On
Expire consents: On
Expire starting on: December 10, 2020
Frequency: Monthly
On November 15, 2020, User1 accepts Terms1 on Device3.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 27
Your company has an Azure Active Directory (Azure AD) tenant named contoso.com. The company has a business partner named Fabrikam, Inc.
Fabrikam uses Azure AD and has two verified domain names of fabrikam.com and litwareinc.com. Both domain names are used for Fabrikam email addresses.
You plan to create an access package named package1 that will be accessible only to the users at Fabrikam.
You create a connected organization for Fabrikam.
You need to ensure that the package1 will be accessible only to users who have fabrikam.com email addresses.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.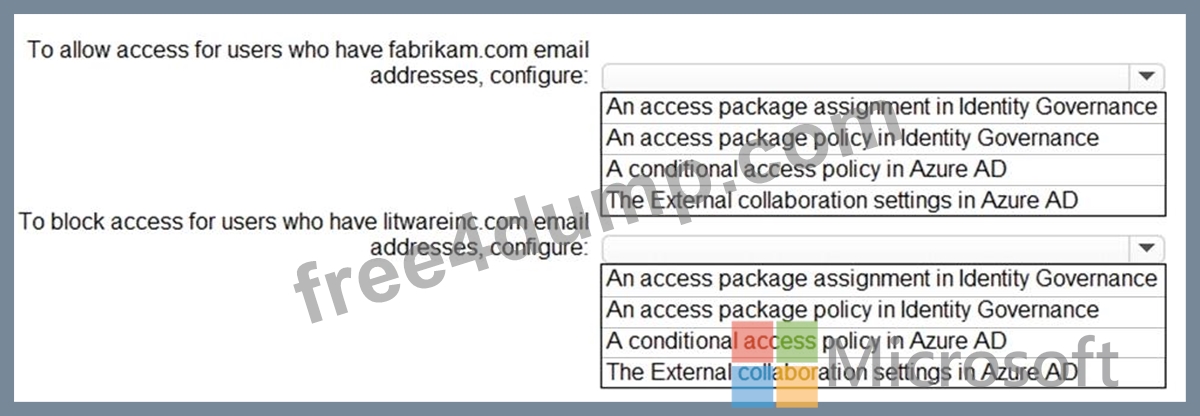
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package-request-policy
https://docs.microsoft.com/en-us/azure/active-directory/governance/entitlement-management-access-package-create
NEW QUESTION 28
You have a Microsoft 365 tenant.
The Azure Active Directory (Azure AD) tenant contains the groups shown in the following table.
In Azure AD. you add a new enterprise application named Appl. Which groups can you assign to App1?
- A. Group2 only
- B. Group1 and Group
- C. Group1 only
- D. Group3 only
- E. Group1 and Group4
Answer: B
NEW QUESTION 29
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant.
You have 100 IT administrators who are organized into 10 departments.
You create the access review shown in the exhibit. (Click the Exhibit tab.)
You discover that all access review requests are received by Megan Bowen.
You need to ensure that the manager of each department receives the access reviews of their respective department.
Solution: You set Reviewers to Member (self).
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION 30
You have an Azure Active Directory (Azure AD) tenant that contains three users named User1, User1, and User3, You create a group named Group1. You add User2 and User3 to Group1.
You configure a role in Azure AD Privileged identity Management (PIM) as shown in the application administrator exhibit. (Click the application Administrator tab.)
Group1 is configured as the approver for the application administrator role.
You configure User2to be eligible for the application administrator role.
For User1, you add an assignment to the Application administrator role as shown in the Assignment exhibit. (Click Assignment tab)
For each of the following statement, select Yes if the statement is true, Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 31
You need to meet the technical requirements for the probability that user identities were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-policies
NEW QUESTION 32
You have a Microsoft 365 tenant.
You need to identify users who have leaked credentials. The solution must meet the following requirements.
* Identity sign-Ins by users who ate suspected of having leaked credentials.
* Rag the sign-ins as a high risk event.
* Immediately enforce a control to mitigate the risk, while still allowing the user to access applications.
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
NEW QUESTION 33
You have a Microsoft 365 tenant.
You need to identify users who have leaked credentials. The solution must meet the following requirements.
* Identity sign-Ins by users who ate suspected of having leaked credentials.
* Rag the sign-ins as a high risk event.
* Immediately enforce a control to mitigate the risk, while still allowing the user to access applications.
What should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
NEW QUESTION 34
You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains an Azure AD enterprise application named App1.
A contractor uses the credentials of [email protected].
You need to ensure that you can provide the contractor with access to App1. The contractor must be able to authenticate as [email protected].
What should you do?
- A. Implement Azure AD Connect.
- B. Run the New-AzureADMSInvitation cmdlet.
- C. Add a WS-Fed identity provider.
- D. Configure the External collaboration settings.
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/external-identities/b2b-quickstart-add-guest-users-portal
https://docs.microsoft.com/en-us/powershell/module/azuread/new-azureadmsinvitation?view=azureadps-2.0
NEW QUESTION 35
Your company has a Microsoft 365 tenant.
All users have computers that run Windows 10 and are joined to the Azure Active Directory (Azure AD) tenant.
The company subscribes to a third-party cloud service named Service1. Service1 supports Azure AD authentication and authorization based on OAuth. Service1 is published to the Azure AD gallery.
You need to recommend a solution to ensure that the users can connect to Service1 without being prompted for authentication. The solution must ensure that the users can access Service1 only from Azure AD-joined computers. The solution must minimize administrative effort.
What should you recommend for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/develop/active-directory-how-applications-are-added
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/require-managed-devices
NEW QUESTION 36
Your company has an Azure Active Directory (Azure AD) tenant named contoso.com.
The company is developing a web service named App1.
You need to ensure that App1 can use Microsoft Graph to read directory data in contoso.com.
Which three actions should yon perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them In the correct order.
Answer:
Explanation:
1 - Add a group claim.
2 - Grant admin consent.
3 - Add delegated permissions.
NEW QUESTION 37
You need to meet the authentication requirements for leaked credentials.
What should you do?
- A. Enable password hash synchronization in Azure AD Connect.
- B. Enable federation with PingFederate in Azure AD Connect.
- C. Configure Azure AD Password Protection.
- D. Configure an authentication method policy in Azure AD.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/security/fundamentals/steps-secure-identity
Topic 2, Contoso, Ltd
Existing Environment
The on-premises network of Contoso contains an Active Directory domain named contos.com. The domain contains an organizational unit (OU) named Contoso_Resources. The Contoso_Resoureces OU contains all users and computers.
The Contoso.com Active Directory domain contains the users shown in the following table.
Microsoft 365/Azure Environment
Contoso has an Azure AD tenant named Contoso.com that has the following associated licenses:
Microsoft Office 365 Enterprise E5
Enterprise Mobility + Security
Windows 10 Enterprise E5
Project Plan 3
Azure AD Connect is configured between azure AD and Active Directory Domain Serverless (AD DS). Only the Contoso Resources OU is synced.
Helpdesk administrators routinely use the Microsoft 365 admin center to manage user settings.
User administrators currently use the Microsoft 365 admin center to manually assign licenses, All user have all licenses assigned besides following exception:
The users in the London office have the Microsoft 365 admin center to manually assign licenses. All user have licenses assigned besides the following exceptions:
The users in the London office have the Microsoft 365 Phone System License unassigned.
The users in the Seattle office have the Yammer Enterprise License unassigned.
Security defaults are disabled for Contoso.com.
Contoso uses Azure AD Privileged identity Management (PIM) to project administrator roles.
Problem Statements
Contoso identifies the following issues:
* Currently, all the helpdesk administrators can manage user licenses throughout the entire Microsoft 365 tenant.
* The user administrators report that it is tedious to manually configure the different license requirements for each Contoso office.
* The helpdesk administrators spend too much time provisioning internal and guest access to the required Microsoft 365 services and apps.
* Currently, the helpdesk administrators can perform tasks by using the: User administrator role without justification or approval.
* When the Logs node is selected in Azure AD, an error message appears stating that Log Analytics integration is not enabled.
Planned Changes
Contoso plans to implement the following changes.
Implement self-service password reset (SSPR). Analyze Azure audit activity logs by using Azure Monitor-Simplify license allocation for new users added to the tenant. Collaborate with the users at Fabrikam on a joint marketing campaign. Configure the User administrator role to require justification and approval to activate.
Implement a custom line-of-business Azure web app named App1. App1 will be accessible from the internet and authenticated by using Azure AD accounts.
For new users in the marketing department, implement an automated approval workflow to provide access to a Microsoft SharePoint Online site, group, and app.
Contoso plans to acquire a company named Corporation. One hundred new A Datum users will be created in an Active Directory OU named Adatum. The users will be located in London and Seattle.
Technical Requirements
Contoso identifies the following technical requirements:
* AH users must be synced from AD DS to the contoso.com Azure AD tenant.
* App1 must have a redirect URI pointed to https://contoso.com/auth-response.
* License allocation for new users must be assigned automatically based on the location of the user.
* Fabrikam users must have access to the marketing department's SharePoint site for a maximum of 90 days.
* Administrative actions performed in Azure AD must be audited. Audit logs must be retained for one year.
* The helpdesk administrators must be able to manage licenses for only the users in their respective office.
* Users must be forced to change their password if there is a probability that the users' identity was compromised.
NEW QUESTION 38
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
For which users can you configure the Job title property and the Usage location property in Azure AD? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 39
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 tenant.
You have 100 IT administrators who are organized into 10 departments.
You create the access review shown in the exhibit. (Click the Exhibit tab.)
You discover that all access review requests are received by Megan Bowen.
You need to ensure that the manager of each department receives the access reviews of their respective department.
Solution: You create a separate access review for each role.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
D18912E1457D5D1DDCBD40AB3BF70D5D
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/create-access-review
NEW QUESTION 40
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AD) tenant that syncs to an Active Directory forest.
You discover that when a user account is disabled in Active Directory, the disabled user can still authenticate to Azure AD for up to 30 minutes.
You need to ensure that when a user account is disabled in Active Directory, the user account is immediately prevented from authenticating to Azure AD.
Solution: You configure conditional access policies.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/choose-ad-authn
NEW QUESTION 41
......
SC-300 Questions Truly Valid For Your Microsoft Exam: https://www.free4dump.com/SC-300-braindumps-torrent.html
SC-300 Actual Questions - Instant Download Tests Free Updated Today!: https://drive.google.com/open?id=1i8nOCREpL0k2OXbOpJPoN2h1m5pC2svJ