


New (2024) Download free SC-200 PDF for Microsoft Practice Tests
100% Free SC-200 Files For passing the exam Quickly
Who are the Microsoft SC-200, Certified professionals?
Microsoft Security Operations Analyst certification is a significant achievement for an IT professional. It is a confirmation of their competence and ability to deal with the challenges of the job. The Microsoft Certified Security Operations Analyst (SC-200) is typically capable of generating security operations reports and analyzing security incidents. They design, implement and maintain the security operations functions within their network or organization. This role requires strong communication skills and good analytical abilities. They also have good computer skills in areas such as databases, operating systems, and networking. Successful candidates usually have at least a bachelor's degree in information technology or a related field. They will often be responsible for managing a team of other IT professionals, and they can expect to carry out tasks such as incident response, intrusion detection, log management, threat analysis, system monitoring, and firewall maintenance. SC-200 exam dumps PDF also covers all the latest questions that appear in the actual test. Outline for advising stakeholders incredible practices referring the improvements.
The role of a Microsoft Security Operations Analyst Certification professional is to ensure that they can protect their organization from all known types of IT risks through the process of identifying vulnerabilities, taking appropriate action to eliminate them, and monitoring new ones as they develop. To do this effectively they need to be able to interpret complex data from many different sources.
Microsoft SC-200 certification exam is an excellent choice for security professionals who want to advance their careers in the field of cyber security. It covers a broad range of topics related to security operations and evaluates the candidate’s abilities to use Microsoft security technologies to secure their organization’s IT environment. By earning this certification, individuals can demonstrate their technical skills and knowledge and gain an edge in the job market.
Microsoft SC-200 exam consists of various topics that are essential for security operations analysts, including threat management, incident response, and governance, risk, and compliance. Candidates are expected to have a solid understanding of security operations fundamentals, such as security tools and technologies, security processes, and security policies. They should be able to analyze security data, identify threats and vulnerabilities, and respond to security incidents effectively.
NEW QUESTION # 147
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Provide global administrator credentials to the litware.com Azure AD tenant.
2 - Create an instance of Microsoft Defender for Identity.
3 - Provide domain administrator credentials to the litware.com Active Directory domain.
4 - Install the sensor on DC1.
Explanation:
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
NEW QUESTION # 148
You have a Microsoft Sentinel workspace that contains an Azure AD data connector.
You need to associate a bookmark with an Azure AD-related incident.
What should you do? To answer, drag the appropriate blades to the correct tasks. Each blade may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 149
DRAG DROP
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation:
Step 1: log in to https://portal.atp.azure.com as a global admin
Step 2: Create the instance
Step 3. Connect the instance to Active Directory
Step 4. Download and install the sensor.
Reference:
https://docs.microsoft.com/en-us/defender-for-identity/install-step1
https://docs.microsoft.com/en-us/defender-for-identity/install-step4
Question Set 3
NEW QUESTION # 150
DRAG DROP
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to configure Azure Security Center to detect possible threats related to sign-ins from suspicious IP addresses to Azure virtual machines. The solution must validate the configuration.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation: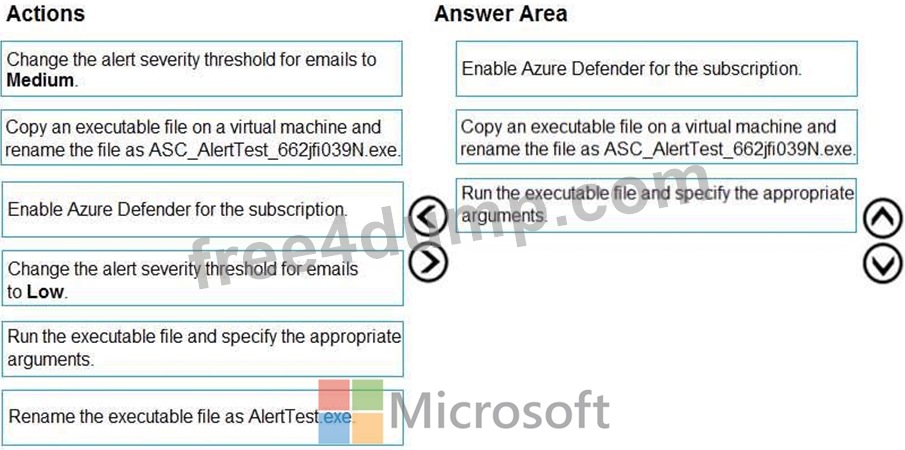
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-alert-validation
NEW QUESTION # 151
You have a Microsoft 365 E5 subscription that contains two users named User! and User2. You have the hunting query shown in the following exhibit.
The users perform the following anions:
* User1 assigns User2 the Global administrator role.
* User1 creates a new user named User3 and assigns the user a Microsoft Teams license.
* User2 creates a new user named User4 and assigns the user the Security reader role.
* User2 creates a new user named User5 and assigns the user the Security operator role.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 152
You have an Azure Sentinel deployment in the East US Azure region.
You create a Log Analytics workspace named LogsWest in the West US Azure region.
You need to ensure that you can use scheduled analytics rules in the existing Azure Sentinel deployment to generate alerts based on queries to LogsWest.
What should you do first?
- A. Deploy Azure Data Catalog to the West US Azure region.
- B. Create a data connector in Azure Sentinel.
- C. Add Microsoft Sentinel to a workspace.
- D. Modify the workspace settings of the existing Azure Sentinel deployment
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/extend-sentinel-across-workspaces-tenants
NEW QUESTION # 153
You plan to create a custom Azure Sentinel query that will track anomalous Azure Active Directory (Azure AD) sign-in activity and present the activity as a time chart aggregated by day.
You need to create a query that will be used to display the time chart. What should you include in the query?
- A. workspace
- B. makeset
- C. extend
- D. bin
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/logs/get-started-queries
NEW QUESTION # 154
You need to create an advanced hunting query to investigate the executive team issue.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Topic 2, Litware inc.
Case study
This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other questions in this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next section of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question in this case study, click the button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the button to return to the question.
Overview
Litware Inc. is a renewable company.
Litware has offices in Boston and Seattle. Litware also has remote users located across the United States. To access Litware resources, including cloud resources, the remote users establish a VPN connection to either office.
Existing Environment
Identity Environment
The network contains an Active Directory forest named litware.com that syncs to an Azure Active Directory (Azure AD) tenant named litware.com.
Microsoft 365 Environment
Litware has a Microsoft 365 E5 subscription linked to the litware.com Azure AD tenant. Microsoft Defender for Endpoint is deployed to all computers that run Windows 10. All Microsoft Cloud App Security built-in anomaly detection policies are enabled.
Azure Environment
Litware has an Azure subscription linked to the litware.com Azure AD tenant. The subscription contains resources in the East US Azure region as shown in the following table.
Network Environment
Each Litware office connects directly to the internet and has a site-to-site VPN connection to the virtual networks in the Azure subscription.
On-premises Environment
The on-premises network contains the computers shown in the following table.
Current problems
Cloud App Security frequently generates false positive alerts when users connect to both offices simultaneously.
Planned Changes
Litware plans to implement the following changes:
Create and configure Azure Sentinel in the Azure subscription.
Validate Azure Sentinel functionality by using Azure AD test user accounts.
Business Requirements
Litware identifies the following business requirements:
The principle of least privilege must be used whenever possible.
Costs must be minimized, as long as all other requirements are met.
Logs collected by Log Analytics must provide a full audit trail of user activities.
All domain controllers must be protected by using Microsoft Defender for Identity.
Azure Information Protection Requirements
All files that have security labels and are stored on the Windows 10 computers must be available from the Azure Information Protection - Data discovery dashboard.
Microsoft Defender for Endpoint requirements
All Cloud App Security unsanctioned apps must be blocked on the Windows 10 computers by using Microsoft Defender for Endpoint.
Microsoft Cloud App Security requirements
Cloud App Security must identify whether a user connection is anomalous based on tenant-level data.
Azure Defender Requirements
All servers must send logs to the same Log Analytics workspace.
Azure Sentinel Requirements
Litware must meet the following Azure Sentinel requirements:
Integrate Azure Sentinel and Cloud App Security.
Ensure that a user named admin1 can configure Azure Sentinel playbooks.
Create an Azure Sentinel analytics rule based on a custom query. The rule must automatically initiate the execution of a playbook.
Add notes to events that represent data access from a specific IP address to provide the ability to reference the IP address when navigating through an investigation graph while hunting.
Create a test rule that generates alerts when inbound access to Microsoft Office 365 by the Azure AD test user accounts is detected. Alerts generated by the rule must be grouped into individual incidents, with one incident per test user account.
NEW QUESTION # 155
You have an Azure Storage account that will be accessed by multiple Azure Function apps during the development of an application.
You need to hide Azure Defender alerts for the storage account.
Which entity type and field should you use in a suppression rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/suppression-rules-for-azure-security-center-alerts-are-now/ba-p/1404920
NEW QUESTION # 156
You have the following advanced hunting query in Microsoft 365 Defender.
You need to receive an alert when any process disables System Restore on a device managed by Microsoft Defender during the last 24 hours.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a detection rule.
- B. Add | order by Timestamp to the query.
- C. Add DeviceId and ReportId to the output of the query.
- D. Create a suppression rule.
- E. Replace DeviceProcessEvents with DeviceNetworkEvents.
Answer: A,C
Explanation:
Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/custom-detection- rules
NEW QUESTION # 157
You have a Microsoft 365 subscription that contains 1,000 Windows 10 devices. The devices have Microsoft Office 365 installed.
You need to mitigate the following device threats:
Microsoft Excel macros that download scripts from untrusted websites
Users that open executable attachments in Microsoft Outlook
Outlook rules and forms exploits
What should you use?
- A. adaptive application control in Azure Defender
- B. attack surface reduction rules in Microsoft Defender for Endpoint
- C. Microsoft Defender Antivirus
- D. Windows Defender Firewall
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/overview-attack-surface-reduction?view=o365-worldwide
NEW QUESTION # 158
You have a Microsoft 365 E5 subscription that contains 200 Windows 10 devices enrolled in Microsoft Defender for Endpoint.
You need to ensure that users can access the devices by using a remote shell connection directly from the Microsoft 365 Defender portal. The solution must use the principle of least privilege.
What should you do in the Microsoft 365 Defender portal? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/respond-machine-alerts?view=o365-worldwide
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/network-devices?view=o365-worldwide
NEW QUESTION # 159
You have an Azure Storage account that will be accessed by multiple Azure Function apps during the development of an application.
You need to hide Azure Defender alerts for the storage account.
Which entity type and field should you use in a suppression rule? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/suppression-rules-for-azure-security-center-alerts-are-now/ba-p/1404920
NEW QUESTION # 160
You have the resources shown in the following table.
You need to prevent duplicate events from occurring in SW1.
What should you use for each action? To answer, drag the appropriate resources to the correct actions. Each resource may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-log-forwarder?tabs=rsyslog
NEW QUESTION # 161
You create an Azure subscription.
You enable Microsoft Defender for Cloud for the subscription.
You need to use Defender for Cloud to protect on-premises computers.
What should you do on the on-premises computers?
- A. Configure the Hybrid Runbook Worker role.
- B. Install the Dependency agent.
- C. Install the Log Analytics agent
- D. Install the Connected Machine agent.
Answer: C
Explanation:
https://docs.microsoft.com/en-us/azure/defender-for-cloud/quickstart-onboard-machines?pivots=azure-arc
NEW QUESTION # 162
You have resources in Azure and Google cloud.
You need to ingest Google Cloud Platform (GCP) data into Azure Defender.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Configure the GCP Security Command Center.
2 - Enable Security Health Analytics.
3 - Enable the GCP Security Command Center API.
4 - Create a dedicated service account and a private key.
5 - From Azure Security Center, add cloud connectors.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-onboard-gcp
NEW QUESTION # 163
DRAG DROP
You have resources in Azure and Google cloud.
You need to ingest Google Cloud Platform (GCP) data into Azure Defender.
In which order should you perform the actions? To answer, move all actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/security-center/quickstart-onboard-gcp
NEW QUESTION # 164
You have a Microsoft 365 subscription that uses Microsoft 365 Defender and contains a user named User1.
You are notified that the account of User1 is compromised.
You need to review the alerts triggered on the devices to which User1 signed in.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 165
You have a Microsoft Sentinel workspace that contains an Azure AD data connector.
You need to associate a bookmark with an Azure AD-related incident.
What should you do? To answer, drag the appropriate blades to the correct tasks. Each blade may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
You can use the Logs blade or incident blade to create a bookmark of an Azure AD-related incident. Once the bookmark is created, you can associate it with the incident by using the incident blade. This allows you to quickly and easily access important information related to the incident in the future.
NEW QUESTION # 166
You need to remediate active attacks to meet the technical requirements.
What should you include in the solution?
- A. Azure Automation runbooks
- B. Azure Logic Apps
- C. Azure Functions
Answer: B
Explanation:
D Azure Sentinel livestreams
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/automate-responses-with-playbooks
Topic 1, Contoso Ltd
Existing Environment
End-User Environment
All users at Contoso use Windows 10 devices. Each user is licensed for Microsoft 365. In addition, iOS devices are distributed to the members of the sales team at Contoso.
Cloud and Hybrid Infrastructure
All Contoso applications are deployed to Azure.
You enable Microsoft Cloud App Security.
Contoso and Fabrikam have different Azure Active Directory (Azure AD) tenants. Fabrikam recently purchased an Azure subscription and enabled Azure Defender for all supported resource types.
Current Problems
The security team at Contoso receives a large number of cybersecurity alerts. The security team spends too much time identifying which cybersecurity alerts are legitimate threats, and which are not.
The Contoso sales team uses only iOS devices. The sales team members exchange files with customers by using a variety of third-party tools. In the past, the sales team experienced various attacks on their devices.
The marketing team at Contoso has several Microsoft SharePoint Online sites for collaborating with external vendors. The marketing team has had several incidents in which vendors uploaded files that contain malware.
The executive team at Contoso suspects a security breach. The executive team requests that you identify which files had more than five activities during the past 48 hours, including data access, download, or deletion for Microsoft Cloud App Security-protected applications.
Requirements
Planned Changes
Contoso plans to integrate the security operations of both companies and manage all security operations centrally.
Technical Requirements
Contoso identifies the following technical requirements:
Receive alerts if an Azure virtual machine is under brute force attack.
Use Azure Sentinel to reduce organizational risk by rapidly remediating active attacks on the environment.
Implement Azure Sentinel queries that correlate data across the Azure AD tenants of Contoso and Fabrikam.
Develop a procedure to remediate Azure Defender for Key Vault alerts for Fabrikam in case of external attackers and a potential compromise of its own Azure AD applications.
Identify all cases of users who failed to sign in to an Azure resource for the first time from a given country. A junior security administrator provides you with the following incomplete query.
BehaviorAnalytics
| where ActivityType == "FailedLogOn"
| where ________ == True
NEW QUESTION # 167
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to configure Azure Security Center to detect possible threats related to sign-ins from suspicious IP addresses to Azure virtual machines. The solution must validate the configuration.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
Answer:
Explanation: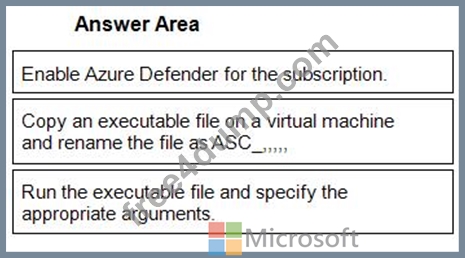
1 - Enable Azure Defender for the subscription.
2 - Copy an executable file on a virtual machine and rename the file as ASC_,,,,,
3 - Run the executable file and specify the appropriate arguments.
Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-alert-validation
NEW QUESTION # 168
......
SC-200 Premium Exam Engine - Download Free PDF Questions: https://www.free4dump.com/SC-200-braindumps-torrent.html
SC-200 Dumps Questions Study Exam Guide : https://drive.google.com/open?id=1llUDkAOLhfNssWRCiaYaeFomn16SrodP